Sep 2, 2026
Enterprise AR Security Risks and Solutions
enterprise-ar-security-risks-and-solutions

AR support can expose more data than phone or chat in a single session. I’d treat it like any other high-risk business system: lock down devices, encrypt session traffic, limit what agents can see, and set strict rules for storage, access, and deletion.
Here’s the short version:
Risk starts at the device: shared phones, tablets, and headsets can be misused if identity checks are weak.
The live session adds new exposure: video, audio, co-browsing, screen share, and AR overlays can show PII, account data, medical details, or payment info.
Web controls matter: weak CSP and Permissions-Policy settings can let bad code run or let the wrong sites use the camera or mic.
Media paths need protection: AR often depends on WebRTC, STUN/TURN, HTTPS, and WSS. If those paths are loose, session data can leak in transit.
Stored records create compliance risk: recordings, transcripts, summaries, and logs need clear access limits, retention periods, and deletion rules.
The fix is simple in principle: use SSO, RBAC, patched devices, DTLS-SRTP, masked fields, consent for remote control, audit logs, and policy reviews tied to HIPAA, ISO 27001, and privacy rules.
If I had to boil the whole article down to 4 priorities, they would be:
Harden endpoints
Encrypt live media and signaling
Restrict co-browsing and recordings
Set firm governance and training
A few facts make the issue plain: one AR session may include video, audio, browser content, AI transcripts, annotations, and audit logs all at once. That’s far more exposure than a voice call. And in fields like healthcare, finance, telecom, and e-commerce, even one bad session can create legal and compliance trouble.
This article explains where those weak spots show up and what I’d put in place to reduce them.
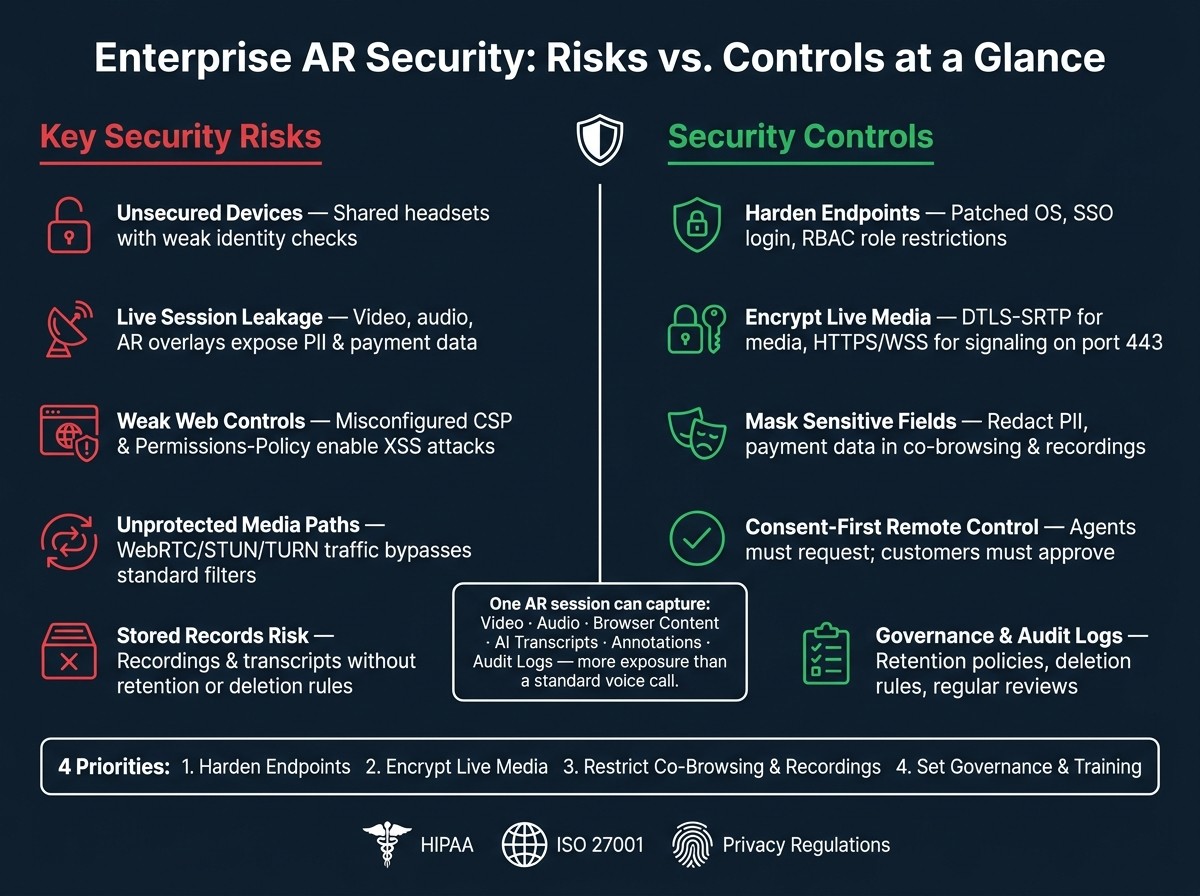
Enterprise AR Security: Risks vs. Controls at a Glance
Common security risks in enterprise AR workflows
These risks tend to fall into three buckets: endpoints, session control, and data handling. Put simply, the weak spots are usually the device, the live session, and the record that gets stored after the call.
Unsecured devices, weak access controls, and session hijacking
Shared headsets and mobile devices can be a problem when no one ties them to a specific agent identity. That makes endpoint misuse much easier. And when teams still rely on older hardware that hasn't received current security patches, they stay exposed to known vulnerabilities.
Authentication issues make this worse. If access controls are weak or split across too many systems, shared devices become easier to abuse. In browser-based AR widgets embedded in enterprise sites, a misconfigured Content Security Policy (CSP) can open the door to Cross-Site Scripting (XSS) attacks that take over an active support session.
Permissions-Policy headers can also create risk when they aren't set up the right way. Without clear restrictions, unauthorized origins may gain access to a device's camera, microphone, or location data during a session.
And even if the endpoint itself is locked down, that doesn't mean the session is safe. Live media can still expose sensitive information.
Data leakage through video, audio, spatial mapping, and co-browsing
Live video, audio, and AI transcripts can pull in more than teams expect. A support call can capture private rooms, spoken sensitive data, and account details, then turn all of that into a stored record.
Co-browsing and screen sharing push the risk even further. If teams don't mask sensitive fields, agents may see private information in the customer's browser or on a shared screen. That same information can also end up inside session recordings. On top of that, recorded overlays and annotations may keep sensitive context about the user's surroundings or device activity.
Once that data moves beyond the live session, the next weak point is how it travels and how long it stays stored.
Network, WebRTC, and compliance gaps in AR support sessions
Many AR platforms use WebRTC for media streaming, along with STUN and TURN services for NAT traversal. The problem is that WebRTC traffic often slips past standard web filters, so media streams need their own routing and inspection controls. If secure media transport isn't in place, audio, video, and screen sharing can be exposed while in transit.
For PHI or financial data, recordings, transcripts, and summaries need clear access, retention, and deletion controls. If that content is stored without the right safeguards, regulated businesses face direct compliance risk.
How to secure AR devices, sessions, and data
These controls close the device, session, and data gaps outlined above.
Harden endpoints and enforce identity controls
Start with the basics. Use supported OS versions and keep devices patched. Give users verified access through SSO, and use RBAC to limit who can launch AR sessions, take remote control, or view recordings.
At the browser layer, use CSP and Permissions-Policy to block injected scripts and limit access to the camera, microphone, and display capture. That matters because once a device is allowed into the session, you don't want extra code or unneeded permissions slipping in through the side door.
Once endpoints are trusted, the next step is to lock down the live session path.
Secure live sessions with strong network and media architecture
Send signaling and API traffic over HTTPS and WSS on port 443. Encrypt media with DTLS-SRTP. Limit outbound traffic to only the STUN and TURN paths you need, and keep TURN over TCP 443 available as a fallback for locked-down networks.
It also helps to log remote control actions and AR pointer use for audit trails. If something goes wrong later, those records show who did what and when.
In practice, that means using:
CSP for script control
DTLS-SRTP for media encryption
SSO/RBAC for access control
TURN over TCP 443 for restricted networks
Permissions-Policy for device access
Limit exposure in co-browsing, screen sharing, and recordings
Co-browsing and screen sharing are where leakage risk tends to pile up. Use field masking or redaction to hide payment details, PII, and other sensitive data during the session and inside recordings.
Remote interaction should never start by default. Agents should request control first, and customers should explicitly approve that request before any remote action begins. That extra click may feel small, but it's often the line between a guided session and an unwanted one.
After the live session ends, control what stays behind. Store recordings in company-controlled storage, restrict access, and apply retention rules.
Governance and compliance controls for enterprise AR
Technical controls help, but they don't solve the whole problem. Policy and oversight matter just as much. Without clear rules behind the tech, even a locked-down AR setup can still open the door to compliance issues. In plain terms, weak governance creates risk all by itself.
Define approved use cases, data flows, and retention rules
Once device and session controls are in place, governance sets the boundaries. It decides which AR support scenarios are allowed and how long session data can stay in your systems.
Start with a clear list of approved AR use cases. Common examples include remote field technician guidance, insurance claim verification, healthcare consultations, and retail support. If a use case isn't approved, it shouldn't be used. That line needs to be simple and firm.
Next, map the data involved in each scenario. That includes video, audio, and shared screen content. Document where that data goes, who can view it, and how long it stays. Use data minimization here: capture only the video, audio, and screen content needed for the session. If the session doesn't need it, don't collect it.
Retention rules also need to be spelled out. Set a clear policy for how long recordings are kept, who can access them, and when they must be deleted. Optional session recordings, paired with a full audit trail, can give teams oversight without piling up extra data risk.
Align AR support with HIPAA, ISO 27001, and privacy requirements
After use cases and retention policies are set, the next step is lining them up with the rules that apply to your industry.
Map AR workflows to HIPAA, ISO 27001, and privacy requirements before launch, then review them on a regular basis. Pick a platform that supports encryption, privacy settings, and audit logging.
Focus on controls such as:
Audit logs
Encryption
Redaction
SSO access control
Secure WebRTC media
AR tools should also be configured with IT and compliance teams before launch. That early setup work can save a lot of trouble later.
Train agents and monitor for misuse
A policy document sitting in a folder won't protect anyone on its own. Agents need training for the moments that matter, especially during live sessions where things can go sideways fast.
Training should cover how to use co-browsing, AR pointers, and screen sharing the right way. It should also cover how to respond to visual cues and keep communication smooth during the session. Supervisors should be able to review transcripts, translations, summarizations, sentiment analysis, and optional session recordings. AI-based sentiment analysis and real-time analytics can flag difficult situations or policy violations, so supervisors can step in fast.
There should also be a clear process for reporting suspicious behavior. Agents need to know what to report, where to send it, and what happens next. Review audit trails on a regular basis, and move suspicious activity through a defined reporting path. Regular reviews, escalation paths, and anomaly alerts help teams catch policy violations early.
Conclusion: Steps toward safer enterprise AR
Enterprise AR isn’t some side channel. It moves video, audio, and screen content across your network in real time. So it should be treated like any other enterprise system, with the same level of security control.
At a practical level, the risk comes down to four priorities: hardened endpoints, encrypted media sessions, restricted co-browsing, and clear governance.
In regulated settings, AR tools should include encryption, privacy controls, and audit logging from the start.
The big shift is simple: treat AR as part of your enterprise security program from day one. Review controls on a regular basis, and train agents before issues show up. That’s what helps keep AR support secure as it scales.
FAQs
How is AR riskier than a phone call?
AR can carry more risk than a standard phone call because it shares live visual data from a user’s surroundings, not just audio. That means private or sensitive details in the customer’s space can be shown by accident.
AR sessions also handle live video and spatial annotations, which adds more points where data could be exposed. To lower that risk, Auvious Video uses enterprise-grade security features such as end-to-end encryption, controlled access permissions, and session recording for auditing and compliance.
What should we secure first in enterprise AR?
Start with data privacy and session integrity. Use end-to-end encryption for all communications so session data stays private from start to finish. Then add role-based access controls and authentication, so only approved users can join or start sessions.
It also helps to use data masking to hide sensitive fields. Back that up with regular audits and compliance with regulations like GDPR and HIPAA.
Do AR sessions create compliance issues?
Yes. Enterprise augmented reality sessions can create compliance issues if they aren’t managed with strong security controls. That’s especially true when sessions involve sensitive visual data and rules such as GDPR, CCPA, and HIPAA.
To cut risk, use platforms with end-to-end encryption, role-based access controls, and data masking. It also helps to back deployments with regular security audits, secure session recordings, and close coordination with IT and compliance teams.